Dashboard
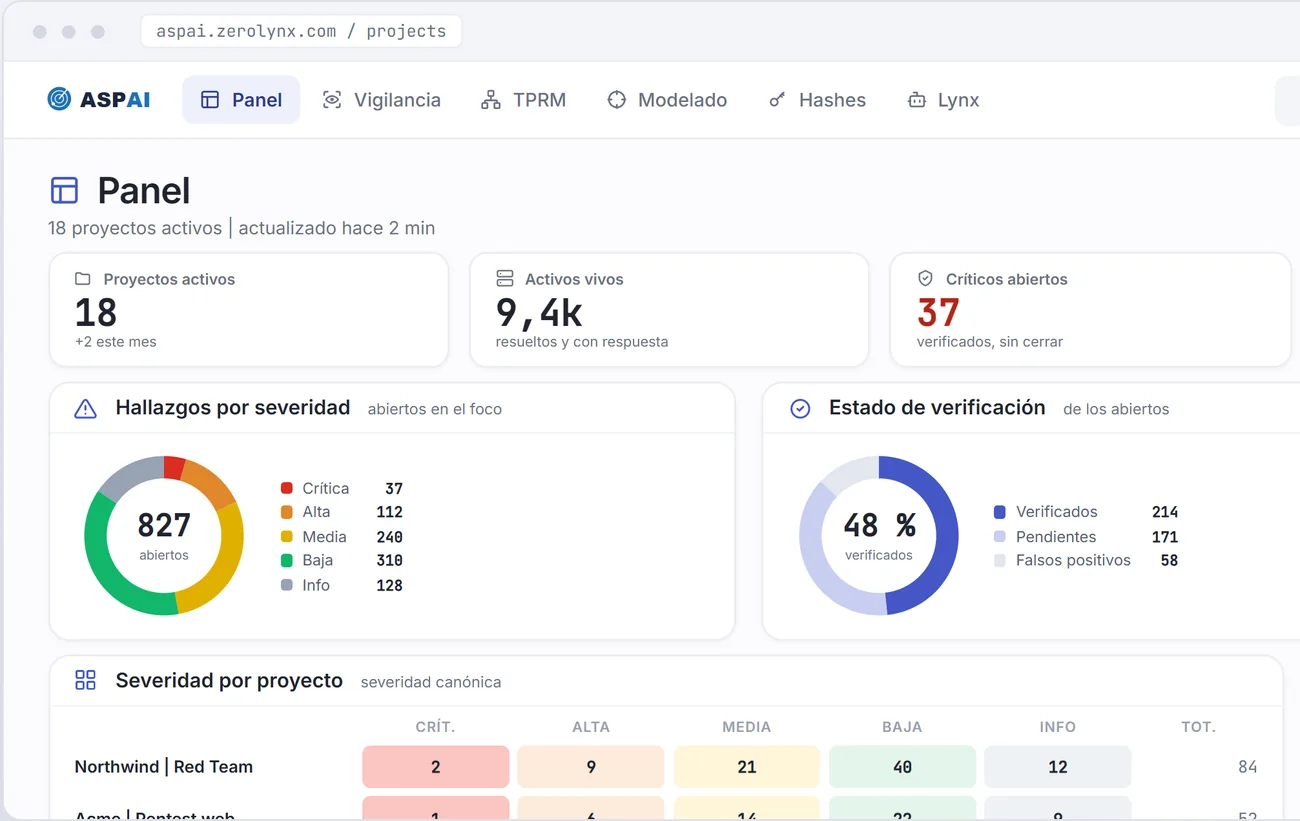
All your projects with severity, verification, trend and what needs attention, in a single view.

Attack Surface Platform | Zerolynx
ASPAI is the Zerolynx platform that brings together reconnaissance, verification, vulnerability management and reporting on the environments you authorise.
You engage it as a service: our team operates it and you see your assets, findings, deadlines and reports through your own access, whenever you need.
Access restricted to authorised users.
ASPAI in action
A tour of the platform. You can pause it, skip forward, go back or watch it full screen with the player controls.
The reel is in Spanish.
One platform, six fronts
The same data from reconnaissance to delivery, for every type of engagement and in one place.
All your projects with severity, verification, trend and what needs attention, in a single view.
The new CVE finds your asset: a technology inventory matched against CVE and KEV, passively and without touching the target.
Your supply chain with a score, a weighted average and a threshold. A supplier with no data never scores zero.
Adversary scenarios, threat hunting and MITRE ATT&CK coverage to measure your detection capability.
The credentials of each engagement, tied to their project, with explicit authorisation and an audit log.
An AI assistant in which each message goes to the model assigned to its action, with tools kept under control.
A service, not another tool
Zerolynx provides the platform and the team. You can see at any time what has been found, what has been verified and what has changed.
We define assets, windows and authorisation. The scope is checked on every action the platform takes.
Passive and active reconnaissance, plus the tests for each engagement: Red Team, penetration testing, code, mobile or generative AI.
Whatever reaches the report has been reproduced, and anything that needs judgement is confirmed by an analyst.
Each delivery is frozen with its date and compared with today: fixed, still open, reappeared or gone.
Access for every role
Your organisation follows the service through its own front end, with the information each role needs.
Exposure status and trend, and open critical risks.
Verified findings with their evidence, deadlines and owners for each fix.
Supply chain ratings against a threshold, for well-founded decisions.
FREQUENTLY ASKED QUESTIONS
Zerolynx’s platform that brings together reconnaissance, verification, vulnerability management and reporting on the environments you authorise. You contract it as a service: our team operates it and you view the results through your own access.
Every serious claim is confirmed with a control test that could have failed, not with an assumption. What reaches the report has been reproduced, and anything that requires judgement is confirmed by an analyst.
Continuously: monitoring cross-checks your technology inventory against every new CVE and the catalogue of known exploited vulnerabilities (KEV), without touching your systems. Offensive campaigns are permanent, not one-off.
Service add-on
Tailored proposal
Tell us which assets and suppliers you want to cover. Zerolynx will prepare a service proposal tailored to your organisation.