Uncensored local AI
Very powerful open-weight models, comparable to frontier models and uncensored: they analyse malware and exploits without refusing and process the evidence automatically.

Forensic kit with local AI | Zerolynx
ForenxIA is a turnkey forensic kit: forensic software, threat databases and generative AI deployed on the computer itself, which processes and analyses the evidence automatically.
It all travels in a rugged, waterproof case, and no evidence, data or question ever leaves for the Internet.
ForenxIA in action
The kit’s full workflow, step by step.
The reel is in Spanish.
Up and running
Recreation of a real session on a practice case: the local AI analyses the cloned disks of a server and a workstation and draws its conclusions on its own.


What is included
We build it, harden it and adapt it to the way you work: it arrives ready for the first case, with all the documentation loaded on the computer itself.
Very powerful open-weight models, comparable to frontier models and uncensored: they analyse malware and exploits without refusing and process the evidence automatically.
Forensic boot, live acquisition, disk and memory analysis and event log hunting. A free or open-source core, with no per-seat licences.
Malware rules, known hashes, antivirus signatures, event log rules and a database of legitimate files, each with its SHA-256 hash.
Procedures adapted to your templates, chain of custody, NDA and expert report templates and a library of official guides.
A video course, forensic courses on TrainIA (FUNDAE format and eIDAS certificates) and in-person practice on a real case.
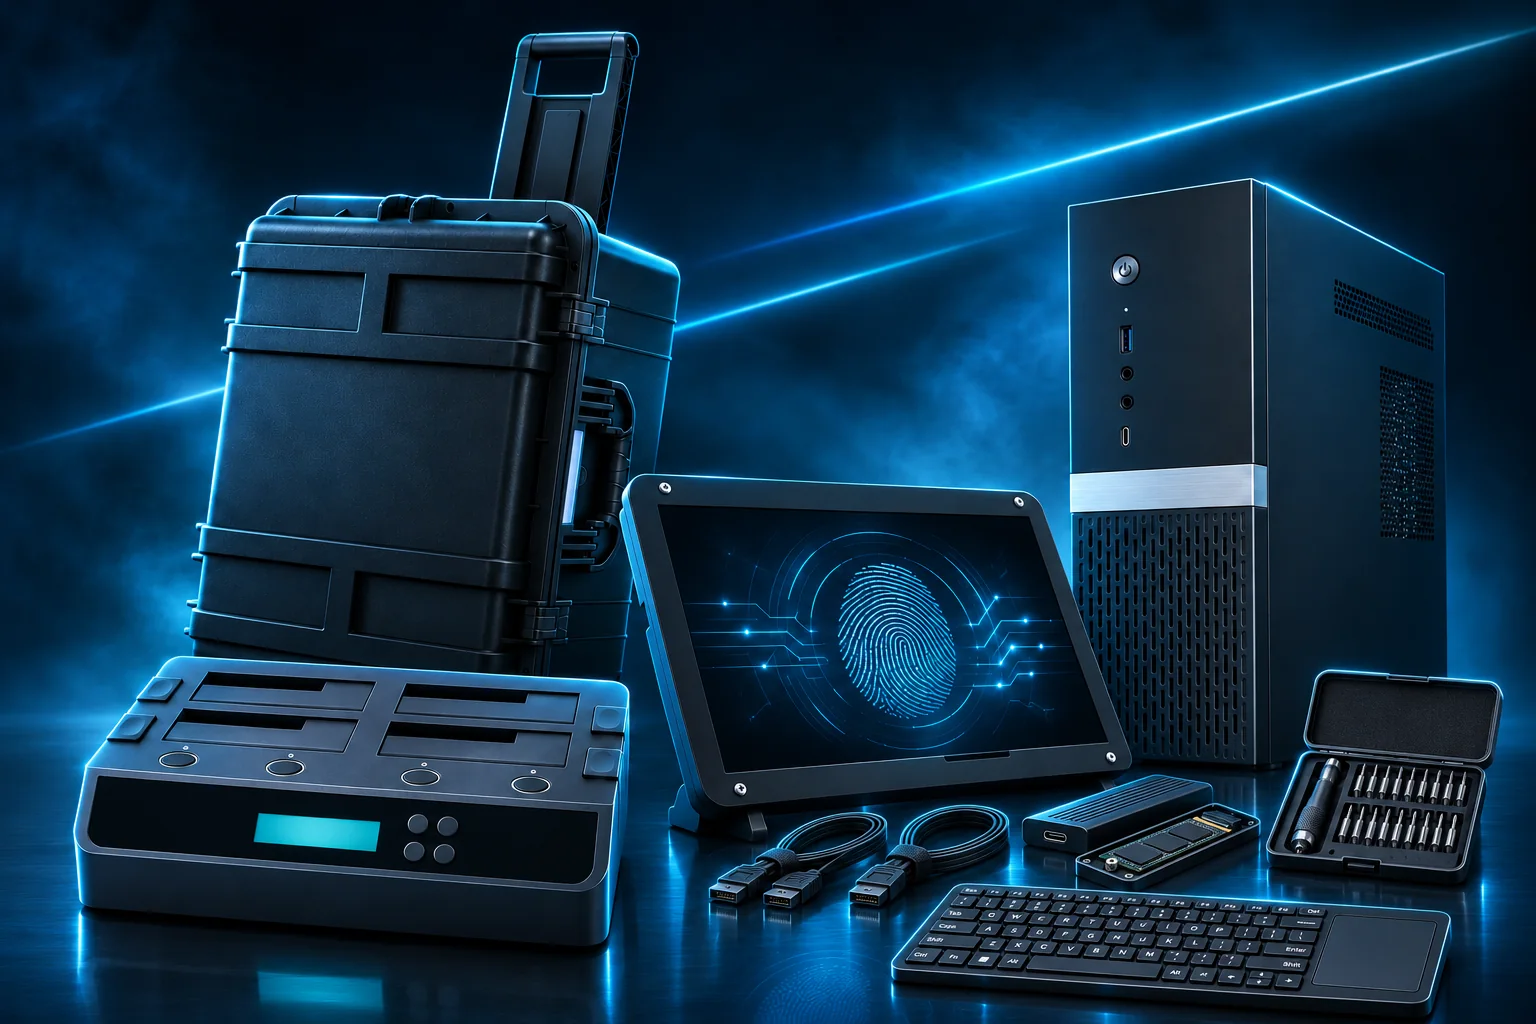
A computer with a dedicated graphics card, duplicator, M.2 readers, touch display and opening kit, in a waterproof case.
What is in the case
Selected to acquire and analyse with full autonomy at the scene.
Workstation power to run the AI locally and process multi-terabyte images.
One drive for the system and models and another only for cases: evidence never mixes with the system.
Clones one disk to three at once without a computer and wipes working disks between cases.
Instant, tool-free connection for M.2 drives from laptops and compact computers.
Aluminium enclosures to work on several M.2 drives in parallel or transport working copies.
With a compact keyboard and mouse, to operate without relying on the client’s equipment.
To open laptops, tablets, phones and consoles without damaging the device or the evidence.
Protection against water, dust and impact in transit, with wheels and a telescopic handle.
The hardware is indicative and may vary depending on parts availability on the market at the time of purchase.
WHAT YOU WILL USE IT FOR
Its procedures cover the most common work of a forensic team, at the scene or in your lab:
Personal data in the evidence is not processed by third-party services (GDPR, NIS2, ENS). Designed by a team certified to ISO/IEC 27001 and ENS HIGH category. See the Trust Center
